First action
Assess active harm, alert the responsible team and preserve minimal useful evidence. A technical compromise requires technical response alongside public-source analysis.


Topic pathway
Inventory public assets, document exposed data, recover accounts and organise proportionate remediation.
Assess active harm, alert the responsible team and preserve minimal useful evidence. A technical compromise requires technical response alongside public-source analysis.
An asset inventory, assigned remediation list, incident timeline and checks showing what has been contained.
Public visibility is not proof of vulnerability. Stay within authorised observation; do not test credentials, expand downloads or scan third-party systems without permission.
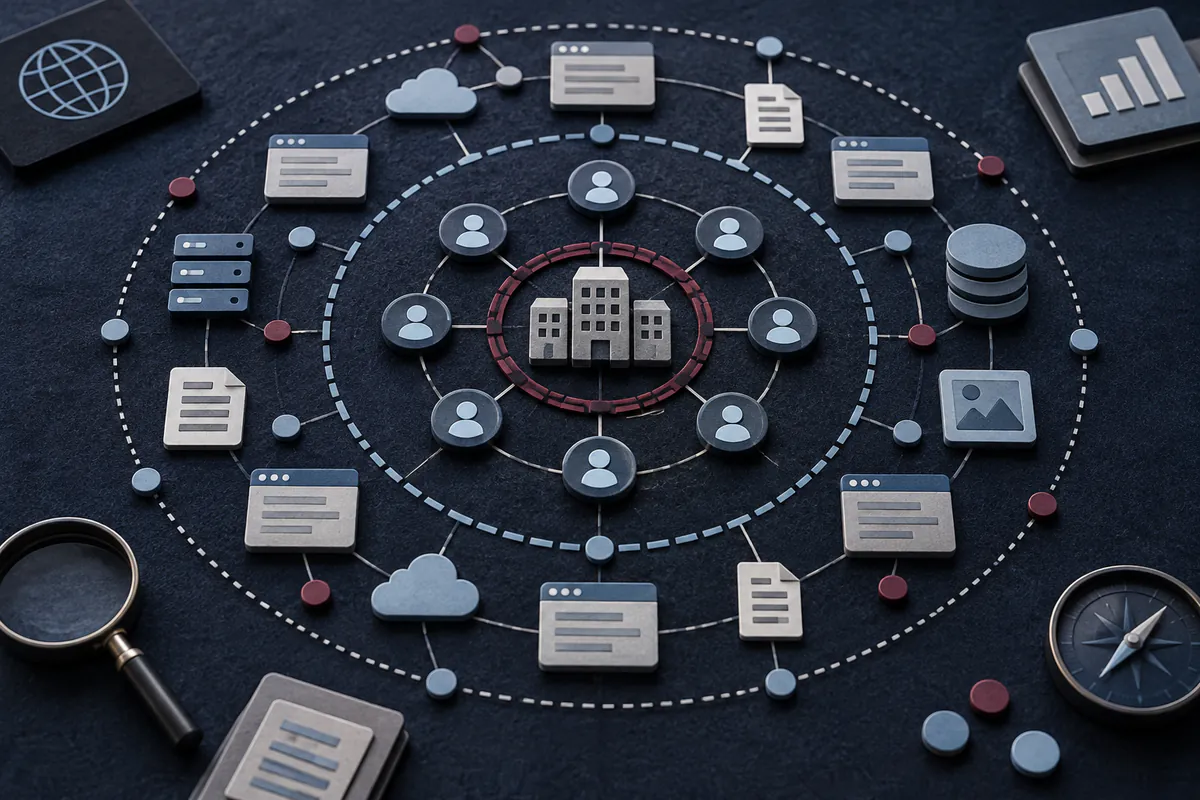

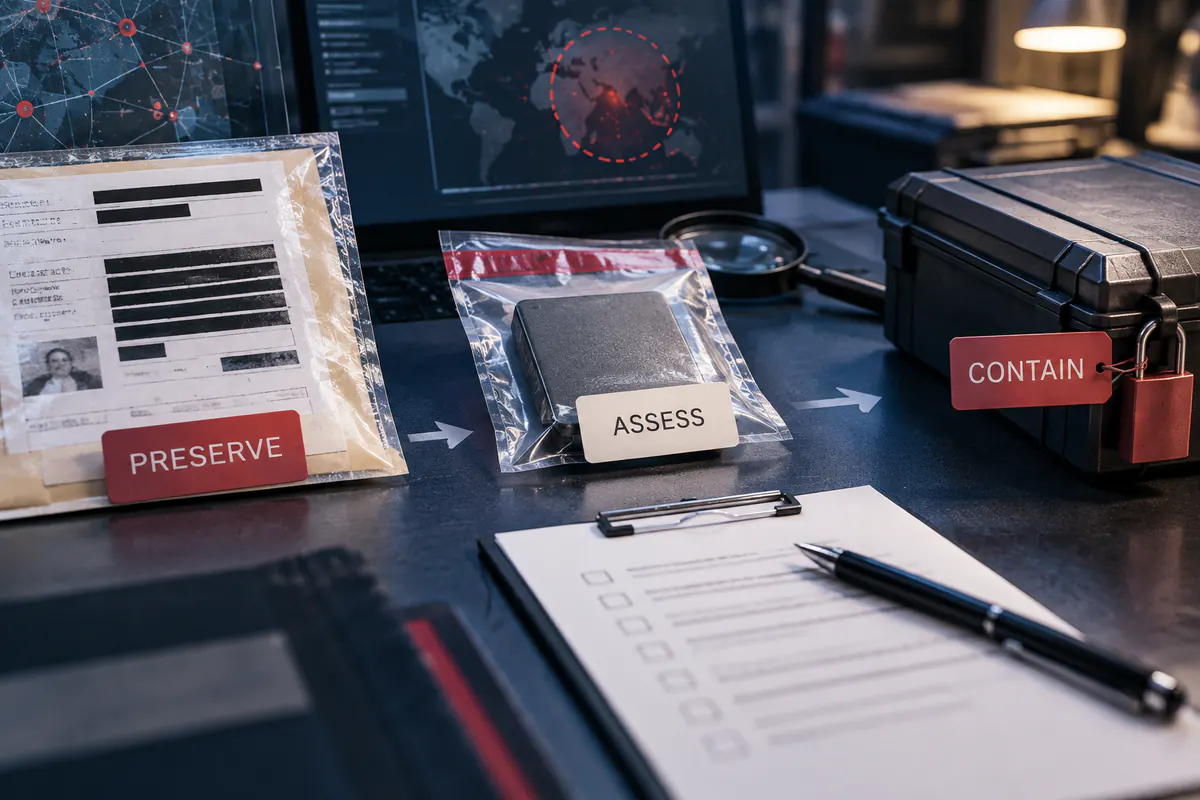
Record the fact being checked, the material reviewed, what remains unknown, the person responsible and the next review trigger. A result is useful when another reader can understand why an action was chosen and what would change it.
| Situation | Check | Record to keep |
|---|---|---|
| Unknown public asset | Confirm owner and function before assessing risk. | Identifier, discovery source, owner and pending-verification status. |
| Accessible sensitive document | Keep minimal context without bulk collection or redistribution. | URL, time, data categories and report to the owner. |
| Potentially compromised account | Separate attempted and successful access; use official recovery. | Alerts, sessions and actions from a trusted device. |
| Vulnerability advisory | Match product and version against authorised inventory and vendor advisory. | Applicability, known exploitation, measure and post-remediation validation. |
Ongoing malicious activity requires technical coordination. Public-source analysis clarifies context but cannot eradicate compromise. Stop collection if it increases exposure or delays containment.
No. Shared hosting, providers and old data can create false associations. Confirm the relationship with a source and owner.
When unauthorised access, malicious action or sensitive exposure is observed. Assessment must examine scope and consequences.
Reading technical evidence
A score alone hides its assumptions. CVSS v4 separates Base, Threat and Environmental metrics.
| Observed item | What it means |
|---|---|
| CVSS-B | Intrinsic severity based on Base metrics. |
| CVSS-BT | Also accounts for Threat metrics. |
| CVSS-BTE | Also incorporates the specified Environmental context. |
Retain version, vector, source and date. Then check product, installed version and exposure conditions before prioritising action.
Fictional learning scenario
A search result displays the title and excerpt of a document described as internal. Current access to the file has not been established.
Indexing is observed. Current availability, exposure scope and possible compromise remain separate questions.
Record URL, excerpt, time and observed scope, then notify the asset owner. Have the authorised team verify access and remediation.
After remediation, check source access separately from the search excerpt. A removed search result alone does not demonstrate that file access has been closed.
An indexed result may be stale. It establishes neither the number of accessible files nor how the exposure occurred.
Further reading

WORLD SOCIAL NETWORKS
After identifying public traces, review who can see posts, account access and shared data to reduce future exposure.