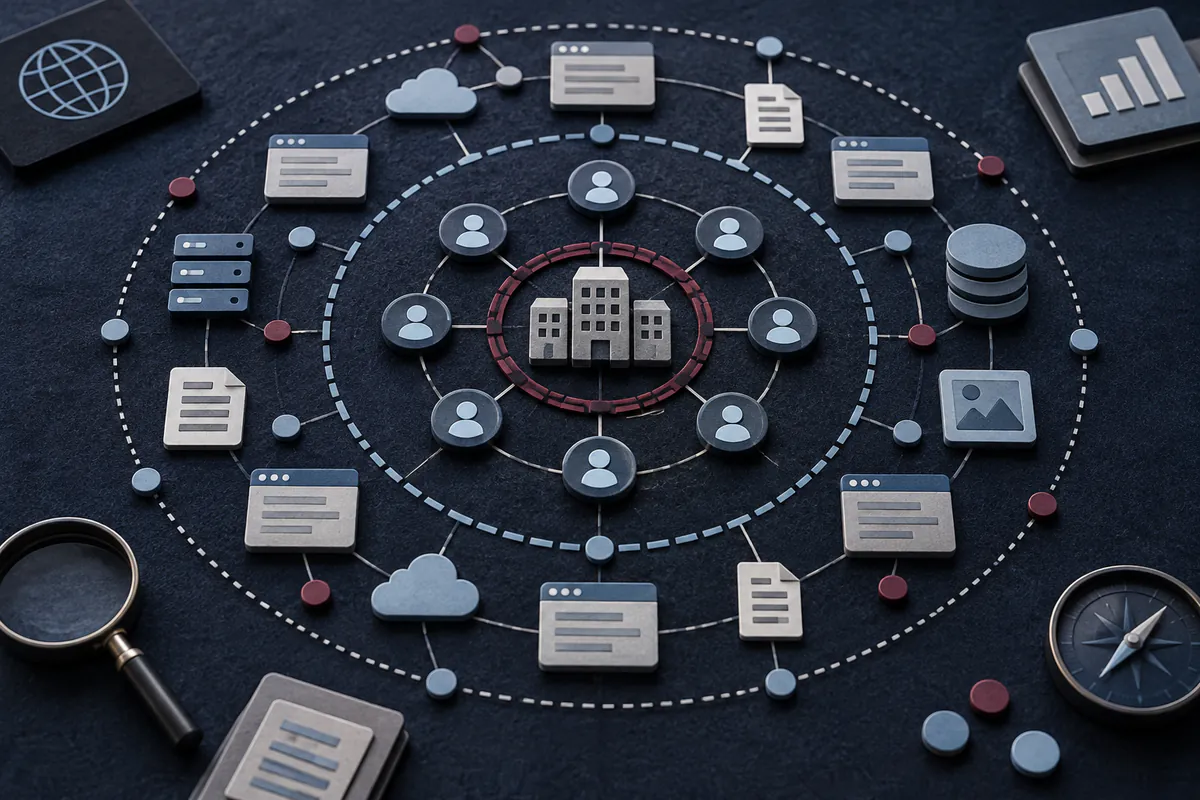
Map public digital infrastructure without mistaking proximity for ownership.
Domains, certificates and network addresses describe dated technical relationships. Linking them can reveal a forgotten asset or an impersonating site, but careless attribution can assign a service to the wrong organisation.
List officially published domains, relevant brands, subsidiaries and countries. Record exclusions and the people authorised to confirm ownership.
2
Collect public traces
Review accessible DNS records, public certificates, web archives and official pages. Record the publisher, observation date and period represented.
3
Connect the evidence
Link each domain, subdomain, certificate, provider and observed page with a precise relationship. Shared hosting or an IP address alone cannot prove common ownership.
4
Grade each asset
Mark assets confirmed, probable, possible or outside scope. Seek independent confirmation before assigning an asset to the organisation.
5
Rank the gaps
Look for expiring domains, old redirects, forgotten login pages, lookalike names and services without a known owner. Judge actual impact before acting.
6
Deliver an actionable inventory
For each asset, state evidence, date, confidence, owner to confirm and proposed action. Technical corrections belong with the authorised team.
A technical relationship is not proof of ownership
Thousands of sites may share a provider, address or protection service. A certificate may also include an old domain or predate a transfer.
Strong attribution combines an official publication, current configuration, consistent history and, where possible, owner confirmation. Preserve the type and date of every link.
The map needs a timeline
DNS and certificate records change. An archive shows a past state; a current response reflects only the time it was checked. Combining periods without labels creates false relationships.
Record discovery date, last observation and original source. A vanished relationship may still matter to a timeline without being called a current exposure.
Turn the map into defensive decisions
The inventory can find an ownerless asset, clarify an official channel or identify a lookalike domain. It is not permission to probe systems.
Connect each risk to an owner, proportionate action and evidence of correction. An unknown asset first needs internal validation.
Read a DNS alias without attributing content
A CNAME describes a DNS alias, not common ownership. Record queried name, target, answer type, resolver and time. IP prefixes, ASNs and registration organisations describe different layers. Hosting providers may serve many customers without controlling their content.
Document the map’s period of applicability
Retain available first and last observations, source and coverage. Recent consultation does not refresh historical evidence. Have authorised owners confirm important assets. After migration, distinguish control of the domain, service and recovery channels.
Reading technical evidence
Date an RDAP event rather than a website’s activity
An RDAP response pairs an event type with a date. Retain both fields together.
Field or situation and its interpretation
Observed item
What it means
eventAction: registration
Registration event for the object; it does not date the website’s first publication.
eventAction: last changed
A change to the registered object; it does not prove a change of owner.
eventDate
Read the date with its UTC offset and the response consultation date.
Record the exact domain and queried service. Corroborate the operator’s identity and publication history separately.
For each point, record what the material actually supports. “Supported” applies to the specific observation, not to the entire case. A contradiction needs explanation; missing material remains an open question.
Define the question
Record the source
Test the observation
State the limits
Entries stay in this page until you leave or reload it. Nothing is saved or submitted by this tool. Use neutral references instead of personal data or credentials.
How to write a useful conclusion
Editorial examples, not findings about your case
Material
Useful wording
Next check
One dated source
The consulted source stated X on the recorded date.
Check its origin and whether it still applies.
Multiple copies of one claim
Several pages repeat X; independent corroboration is missing.
Find the original and a source with independent evidence.
Conflicting sources
A states X while B states Y; the difference is unresolved.
Compare dates, scope, identifiers and definitions.
No matching result
No result was found in the recorded scope.
Describe queries, coverage and access limitations.
What to check and what to record
Use this grid to turn the method into a reviewable case file. A missing item remains an open question. The interpretation limit prevents a finding from becoming an unsupported conclusion.
Topic-specific checks
Check
Useful record
Interpretation limit
DNS
Record type, resolver, value and observation time.
A current answer does not describe the full domain history.
Hosting
Observed address, ASN and association source.
CDNs, cloud and shared hosting limit attribution.
Certificates
Covered names and logging or validity dates.
A logged certificate does not prove a currently active service.
Common pitfalls
Four shortcuts that weaken the result.
Attributing by IP
A shared address may connect unrelated organisations.
Treating archives as current
An old capture does not establish an active service.
Scanning without permission
Open-source mapping does not authorise testing systems.
Publishing a sensitive inventory
The list could aid impersonation; limit its circulation.
Practical questions
Frequently asked questions.
Can a certificate identify a domain owner?
It can provide a clue, but its names and date alone do not establish current ownership.
Does a shared IP mean a shared organisation?
No. Shared hosting, content delivery and protection services make this inference unreliable.
Should a scan be used to complete the map?
Only under a separately authorised technical scope. This guide uses public traces and owner validation.
Public references
These primary references support the checks described here. The sequence and working sheet are an IIS editorial method; a cited organisation does not endorse this guide. Read each reference within its stated date, jurisdiction and scope.
ICANN — RDAP. Official context for domain registration lookup and its limits.
RFC 1034. Reference for the technical fields and interpretation boundaries described in this guide.
Editorial scope
Published by Internet Intelligence Service on 23 September 2026. Last content update: 29 October 2026. This educational guide describes a lawful, defensive method. It is not legal advice, an emergency service or authority instruction.