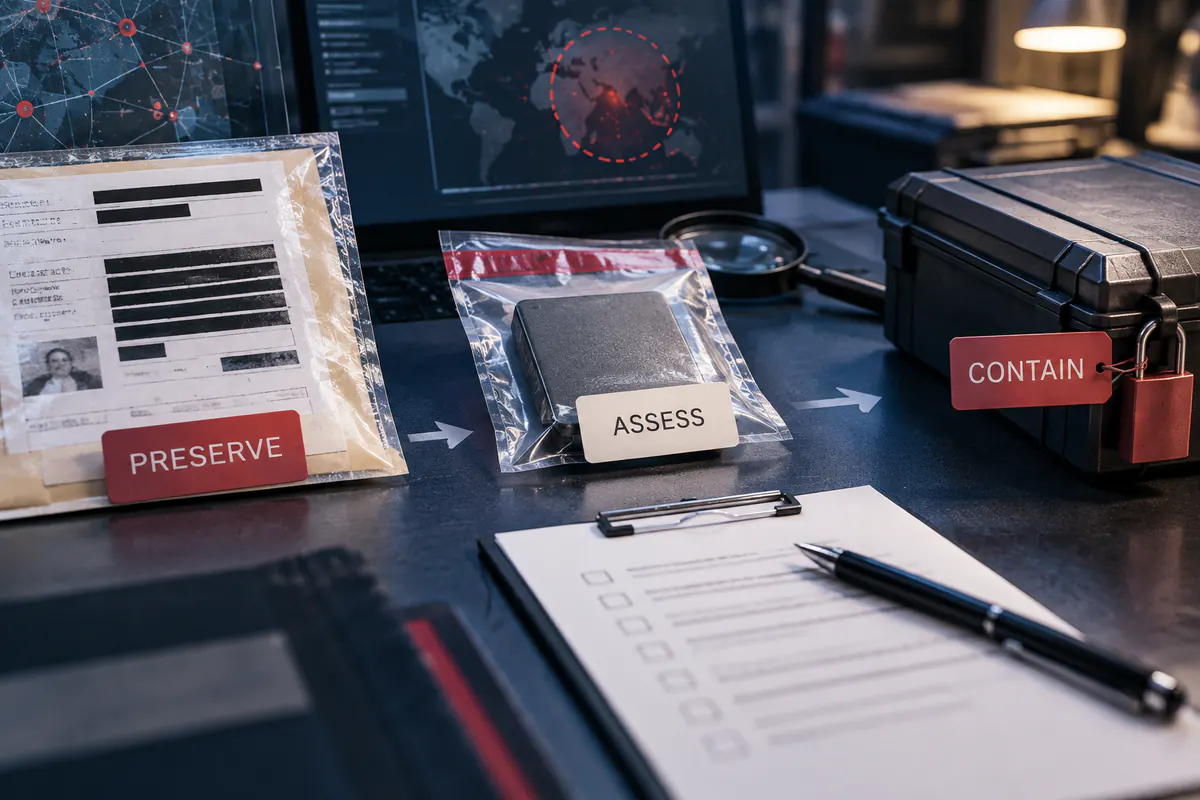
Document a public data exposure without increasing its distribution.
The first objective is not to download everything. Confirm public access, assess scope cautiously, preserve proportionate evidence and activate the right response owners.
Record the address, date, access path and the smallest evidence needed to establish exposure. Do not explore directories or accounts that are not clearly public and authorised.
2
Classify visible data
Identify broad categories such as contact details, credentials, documents, technical secrets, financial records or vulnerable people. Avoid copying their content.
3
Estimate without scraping
Use limited indicators of volume, period, indexing and accessibility. A cautious range is better than mass collection that creates another sensitive copy.
4
Preserve proportionate evidence
Keep the URL, useful headers, contextual capture and observation metadata. Redact working copies while protecting any necessary original.
5
Reduce exposure
Alert the technical owner safely, remove public access or indexing when authorised, and avoid announcements that make the issue easier to find before remediation.
6
Organise the response
Maintain a timeline, identify affected people and duties, then involve security, legal, privacy, insurance and communications teams as appropriate.
Prove the issue without duplicating the harm
Exposure does not authorise downloading, testing or redistribution. Evidence should answer where, when and how access was observed.
Define a minimal sample, restrict case access and log transformations. Working copies can be redacted when full content is unnecessary.
Separate visibility, indexing and compromise
An indexed page, misconfigured storage and compromised account are different incidents. Do not infer technical origin from the visible outcome alone.
Keep observed, potential and confirmed scope separate to avoid overstatement and guide authorised technical checks.
Prioritise consequences for people
Authentication, health, financial, location or child-related data may need urgent action. Nature and context matter as much as record count.
Communication should help people protect themselves without revealing new exploitable detail or claiming an unconfirmed source or volume.
Check the disclosure channel
A security.txt file may identify contact, expiry and disclosure policy. Check origin and scope. It does not grant blanket testing permission. An address inside exposed data does not establish authority to receive a report.
Separate exposure from historical access
An accessible URL establishes a dated observation, not the number of viewers. Historical access requires authorised teams and logs. Supply exact resource, time, general exposure type and observation method without browsing additional folders to measure scope yourself.
Worked example
A sensitive document is accessible through a public link
Fictional teaching case, not a client investigation.
What minimum evidence permits an owner alert without increasing exposure?
Observation, interpretation and limit
Observation
What it establishes
What remains unproven
A public URL returns a document containing personal contact details.
The document is accessible under this consultation’s conditions.
This does not establish who accessed it previously or when exposure began.
The file indicates several sheets, but only the first was examined.
Observed scope is limited to one sheet.
Other contents remain unknown; do not invent an affected-person count.
The owner removes public access after the report.
A limiting measure is announced and can be checked.
Removal does not prove absence of earlier copies or resolution of every cause.
Conclusion to record
Report the URL, access conditions, time and observed data categories to the owner. Preserve only necessary context; leave scope and duty assessment to the relevant team.
What would change the conclusion?
Check the authorised access restriction and request assessment results; record observations rather than guaranteeing erasure everywhere.
Check your reasoning
Is discovery time the beginning of exposure? Which records would be needed to narrow that interval?
For each point, record what the material actually supports. “Supported” applies to the specific observation, not to the entire case. A contradiction needs explanation; missing material remains an open question.
Define the question
Record the source
Test the observation
State the limits
Entries stay in this page until you leave or reload it. Nothing is saved or submitted by this tool. Use neutral references instead of personal data or credentials.
How to write a useful conclusion
Editorial examples, not findings about your case
Material
Useful wording
Next check
One dated source
The consulted source stated X on the recorded date.
Check its origin and whether it still applies.
Multiple copies of one claim
Several pages repeat X; independent corroboration is missing.
Find the original and a source with independent evidence.
Conflicting sources
A states X while B states Y; the difference is unresolved.
Compare dates, scope, identifiers and definitions.
No matching result
No result was found in the recorded scope.
Describe queries, coverage and access limitations.
What to check and what to record
Use this grid to turn the method into a reviewable case file. A missing item remains an open question. The interpretation limit prevents a finding from becoming an unsupported conclusion.
Topic-specific checks
Check
Useful record
Interpretation limit
Observed access
URL, time, data type and observed access state.
Do not test credentials or access neighbouring folders.
Scope
Minimal lawful sample and potentially affected categories.
An exfiltration claim is not a confirmed leak.
Containment
Notified owner, action taken and closure evidence.
Public removal does not establish that no earlier copy exists.
Common pitfalls
Four shortcuts that weaken the result.
Downloading everything
Mass collection creates a sensitive copy and may exceed necessity or authority.
Publishing raw evidence
A screenshot or public link can amplify exposure.
Equating exposure with attack
Origin and method require authorised investigation.
Announcing a precise volume too soon
Indexing or pagination indicators may not prove the real record count.
Practical questions
Frequently asked questions.
Should one data example be retained?
Only where necessary to establish exposure, in the smallest quantity and restricted storage.
Should visible people be contacted directly?
Not without scoping. Poorly planned notification can expose more data or disrupt the response.
Is public data harmless?
No. Aggregation, context or linkage to a person can create new risk.
Public references
These primary references support the checks described here. The sequence and working sheet are an IIS editorial method; a cited organisation does not endorse this guide. Read each reference within its stated date, jurisdiction and scope.
CNIL. Breach documentation and notification criteria; assess the actual context.
RFC 9116 — security.txt. Reference for the technical fields and interpretation boundaries described in this guide.
Editorial scope
Published by Internet Intelligence Service on 15 September 2026. Last content update: 29 October 2026. This educational guide describes a lawful, defensive method. It is not legal advice, an emergency service or authority instruction.